SERVICE / 02

Know whether controls still hold.

Targeted security testing that follows change, validates important controls, and turns findings into decisions.

Cadence scoped to your release cycle

Have a particular question about this work?

Explore a guide and refine the focus ↗

WHO IT IS FOR

For teams whose environment changes faster than an annual assessment can reflect.

A point-in-time report can be accurate on delivery and stale after the next release. Security needs a repeatable way to test the assumptions that matter most.

THE WORK

From question to evidence.

  1. Agree on the systems, attack paths, and business risks worth testing.
  2. Test controls in the context of how the environment actually operates.
  3. Separate exploitable issues from scanner noise and explain business impact.
  4. Recheck important fixes and adjust the next cycle as the environment changes.

WHAT YOU TAKE AWAY

Actionable findings, clear priorities, and evidence that critical controls work as intended.

AN EXAMPLE OF THE OUTPUT

Explore the deliverable.

Compare engagements ↗

ILLUSTRATIVE SAMPLE / FICTIONAL ENGAGEMENT

Customer-review response

Turn a broad security claim into a supported answer.
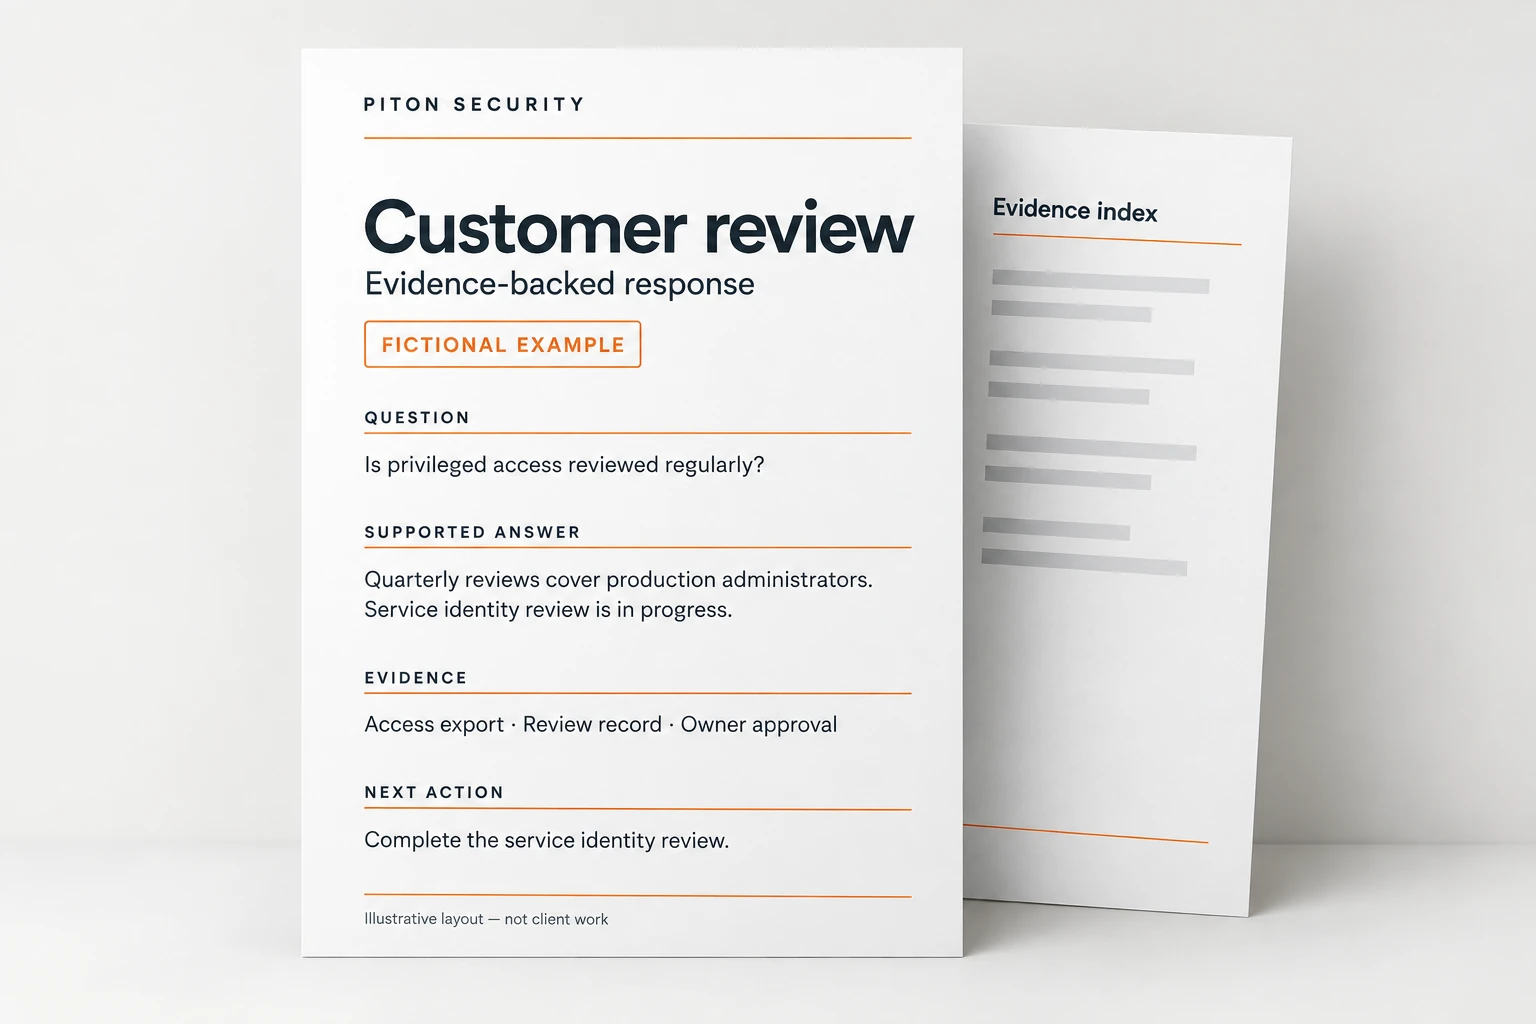
Fictional customer-review response document with supported answer, evidence, and next action.
Fictional document mockupView full size ↗
Question or test
Customer asks: “Is privileged production access reviewed regularly?”
Response or finding
Access reviews run quarterly. The latest review covered the production administrator group and recorded owner sign-off. Service identities are tracked separately; their review is still in progress.
Evidence and consequence
A dated access export, review record, approval, and removal ticket support the human-access claim. The service-identity gap is recorded rather than hidden.
Follow-up and reusable answer
Next action
Assign an owner to finish the service-identity review and agree on how to communicate that gap to the customer.
Reusable record
Keep the approved answer with its evidence date, scope, owner, and review date so the next response can be checked before reuse.
ILLUSTRATIVE SAMPLE / FICTIONAL ENGAGEMENT

Validation finding

A revoked service credential still reaches a production API.

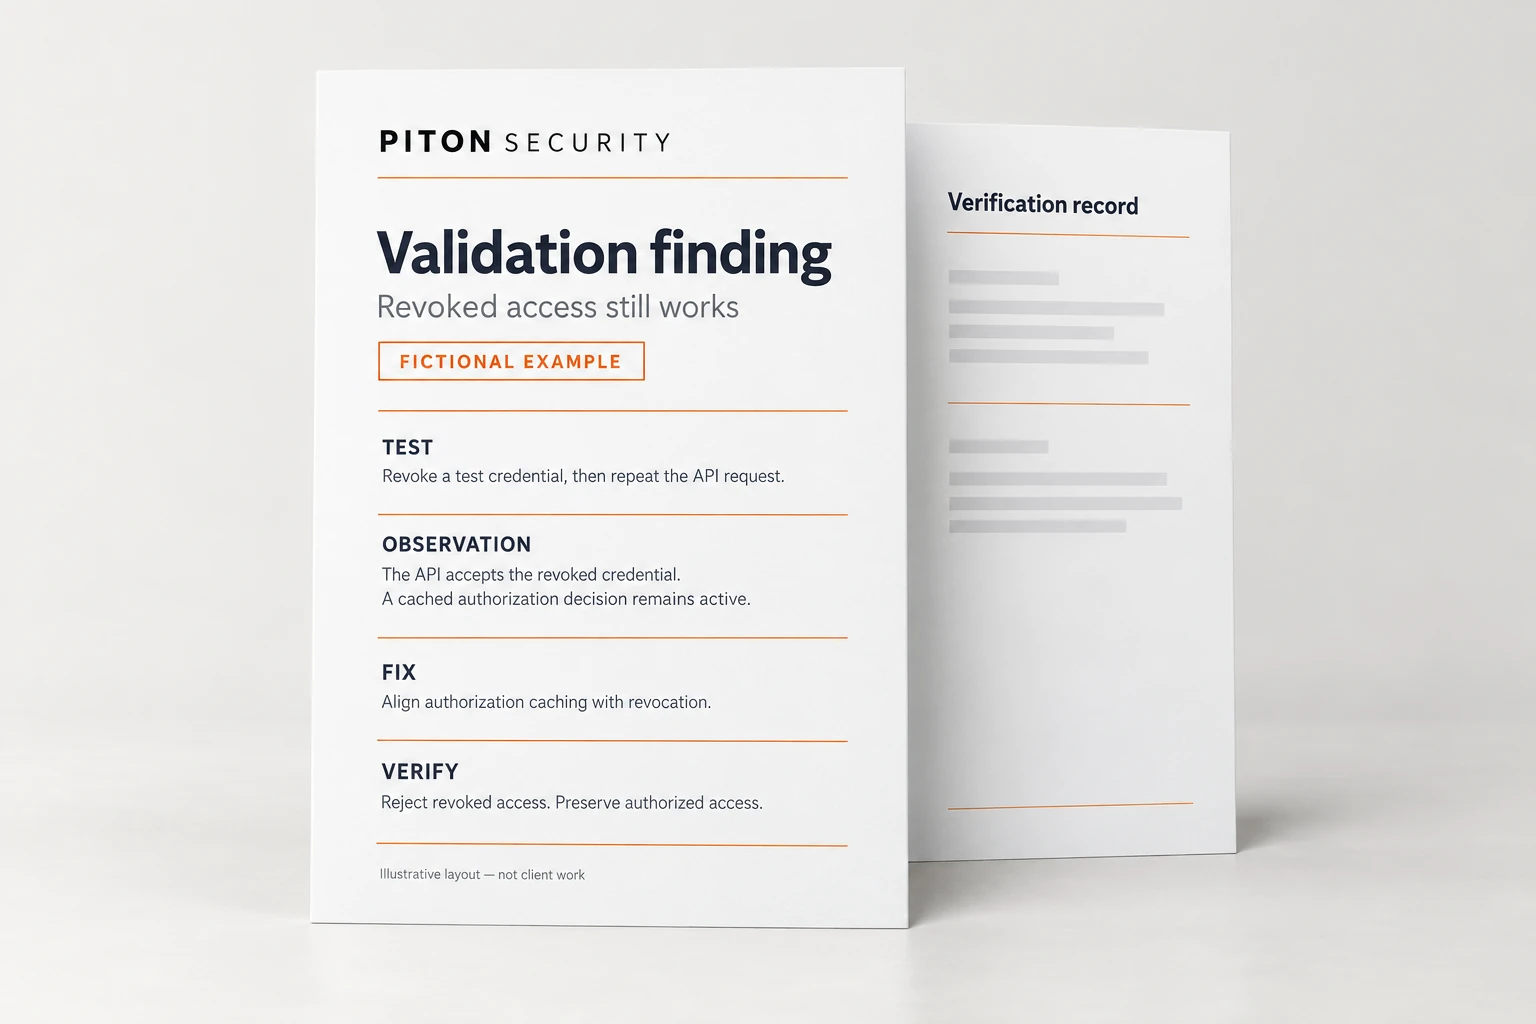
Fictional validation report with test, observation, fix, and verification sections.
Fictional document mockupView full size ↗
Question or test
Test: revoke a designated test credential, then repeat its previously permitted API request.
Response or finding
The identity service records the credential as revoked, but the API continues accepting it through a cached authorization result.
Evidence and consequence
The revocation timestamp and repeatable request/response show a gap between the identity state and the API’s enforcement. The report records the tested window and affected endpoint.
Fix and verification plan
Fix
Align API authorization and cache invalidation with credential revocation. Assign the change to the relevant application and identity owners.
Retest
Repeat the same revocation sequence and check the affected API. Confirm revoked access is rejected and an authorized credential still works.

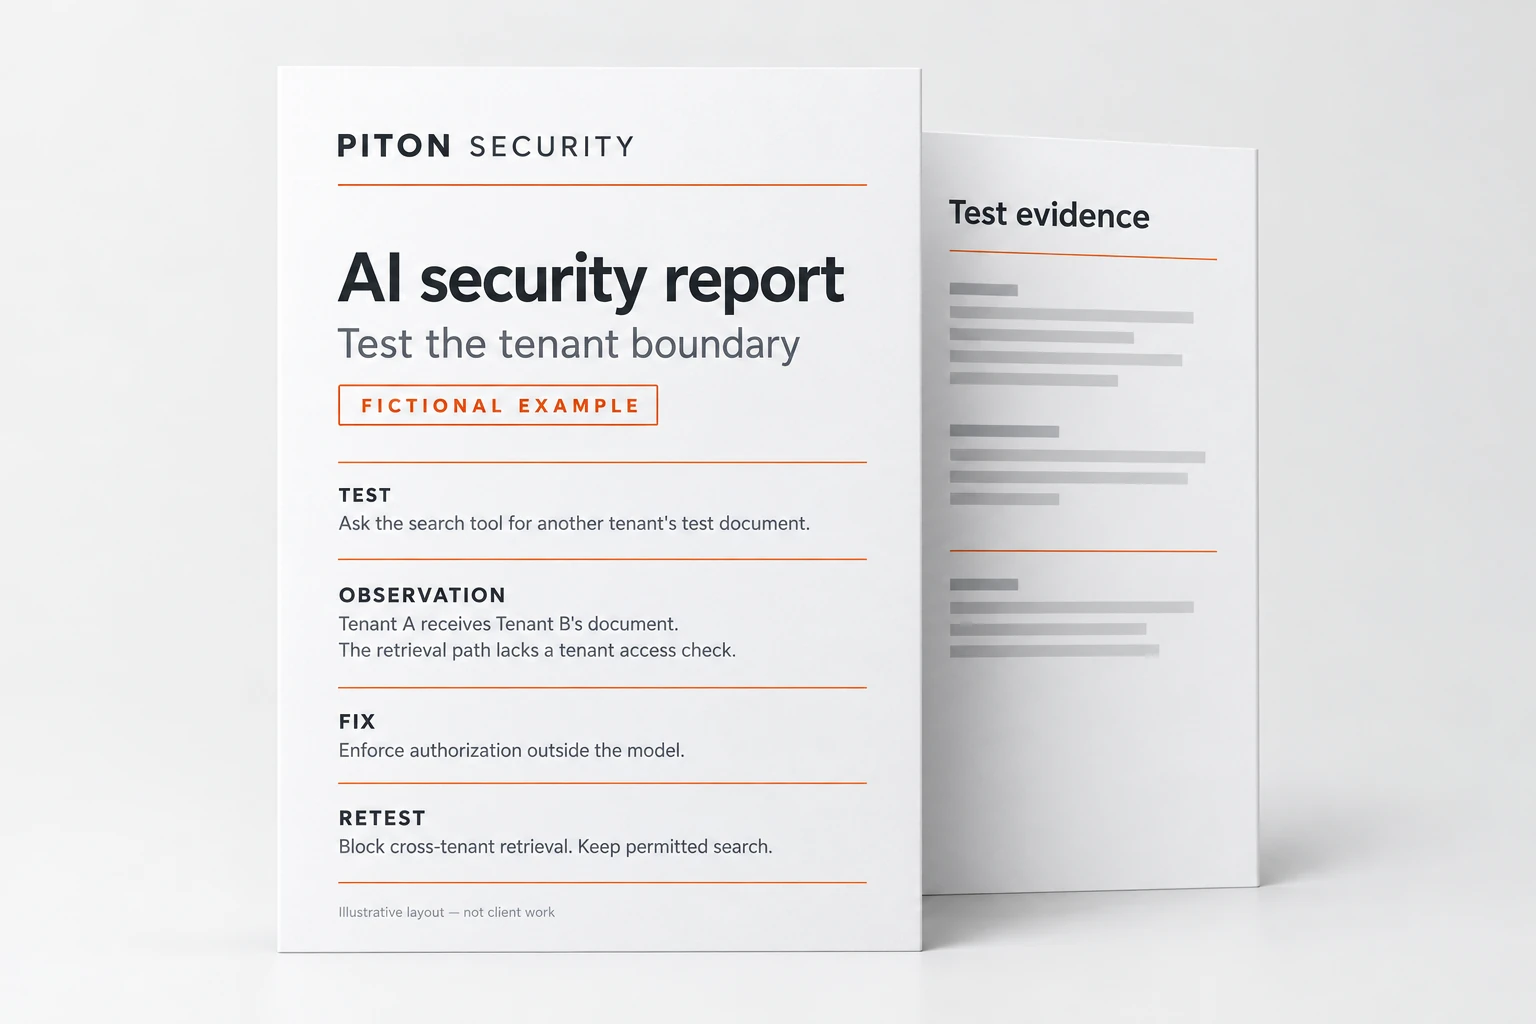
ILLUSTRATIVE SAMPLE / FICTIONAL ENGAGEMENT

AI application test report

A support assistant returns another tenant’s document.

Fictional AI security report describing a cross-tenant retrieval test and retest.
Fictional document mockupView full size ↗
Question or test
Test: use an account in tenant A to request a test document belonging to tenant B through the assistant’s search tool.
Response or finding
The tool returns tenant B’s test document. The application checks login but does not enforce tenant access on the retrieved document.
Evidence and consequence
A signed-in customer could read another customer’s information through the support workflow. The finding records the test identities, retrieval path, and observed boundary failure.
Fix and verification plan
Fix
Enforce authorization on every tool request and returned document using the authenticated user and tenant. Keep that check outside the model.
Retest
Repeat the cross-tenant request with the original account and alternate inputs. Confirm unauthorized content is withheld and permitted searches still work.

ILLUSTRATIVE SAMPLE / FICTIONAL ENGAGEMENT

Leadership roadmap

Give the next quarter three owned security decisions.

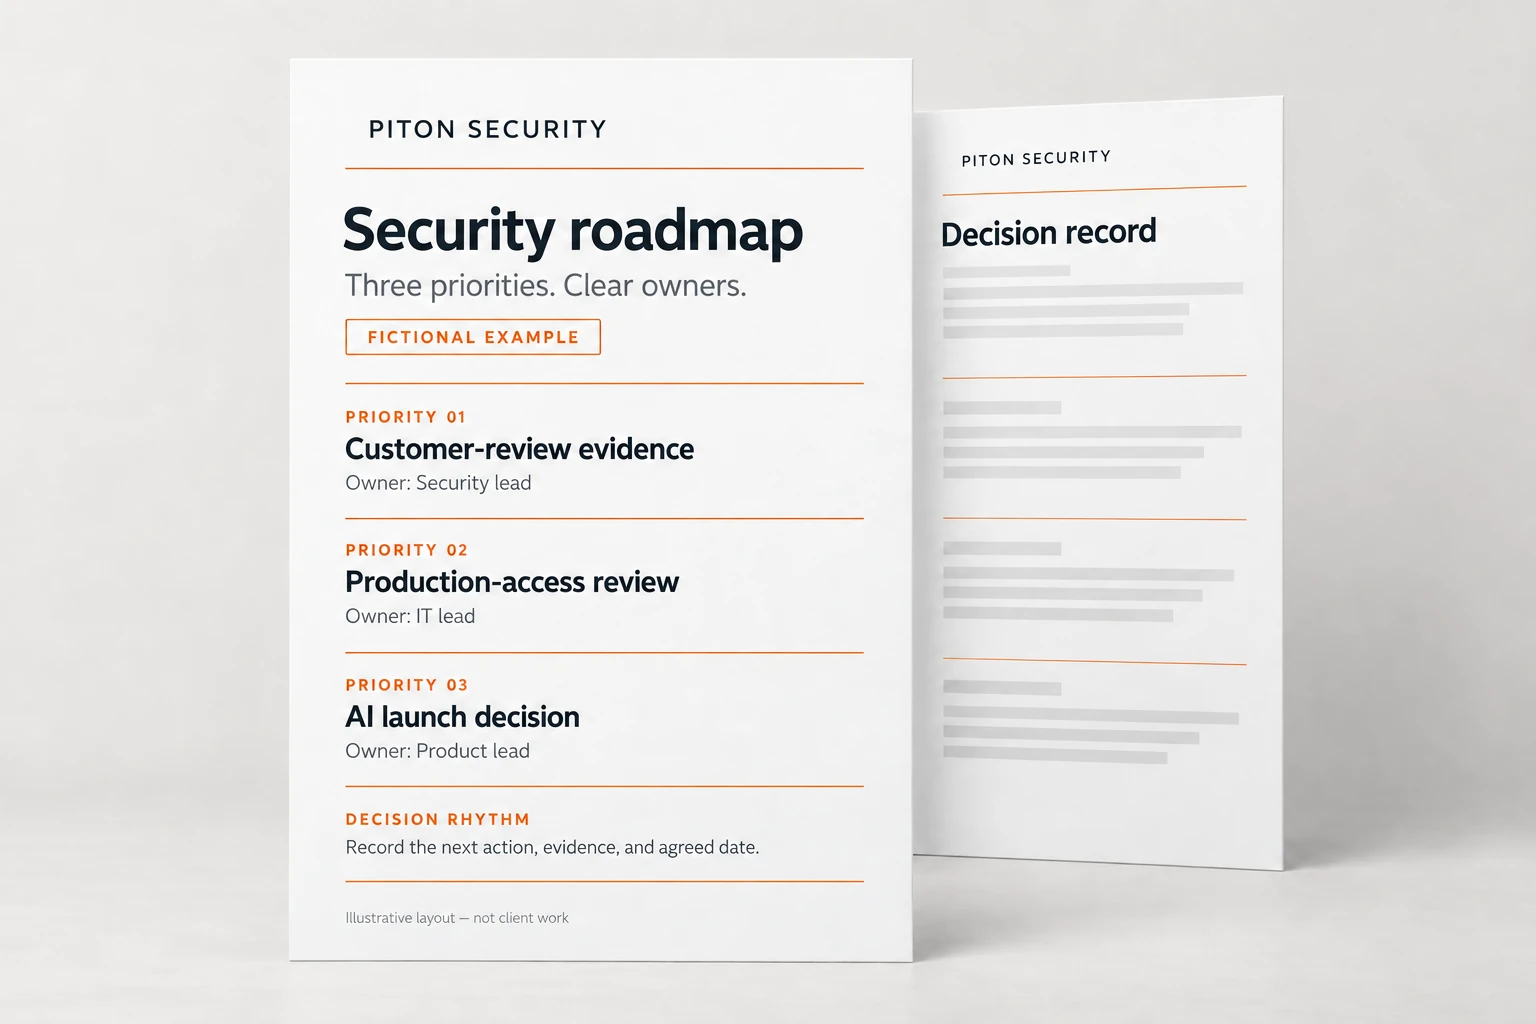
Fictional security roadmap with three priorities and accountable owners.
Fictional document mockupView full size ↗
Question or test
Decision: prioritize customer-facing security commitments alongside a growing product team’s existing work.
Response or finding
Start with three priorities: ownership of customer-review evidence, the production-access review, and the AI launch decision. Record an accountable owner and the evidence each decision needs.
Evidence and consequence
The roadmap connects each priority to a business decision, a control owner, and a check-in date. Unresolved assumptions remain visible rather than being presented as completed work.
Ownership and decision rhythm
Action record
For each priority, record the owner, next action, evidence required, dependencies, and the decision date agreed with the team.
Leadership update
Use a regular review to show what changed, what remains blocked, and which decision needs leadership attention. Adjust priorities as the business changes.

PRACTICAL QUESTIONS

Before we begin.

Prepare a scope brief ↗
How is this different from one annual assessment?

The cadence follows changes in the environment. Each cycle focuses on agreed systems, attack paths, and controls, then adjusts the next cycle using the findings and release changes.

Can testing involve production systems?

The environment, permitted activities, and boundaries are defined when scoping the work. Bring production constraints to the conversation so the testing approach can be agreed.

What happens after we fix a finding?

Important fixes are rechecked, and the next cycle is adjusted as the environment changes. The specific retest boundaries and timing are part of the scope.

What does a passing test tell us?

It provides evidence about the controls and paths tested under the recorded conditions. The report should distinguish that evidence from systems or conditions outside the test scope.

NEXT STEP

Talk through the scope.

Share the situation and the decision it needs to support.

Email Piton ↗

YOUR RECORD AND QUESTION COUNTS

Privacy preferences

Page adjustments are on by default unless your browser sends Global Privacy Control. Your saved starting point, answers, reading history, and inferred interests are kept in this tab’s browser session. Closing the tab ends the session; browser session restore may bring it back. Only the off preference is saved persistently. AI guides send the situation and follow-up choices you select to a server-side writer through OpenRouter. On the guide page you can also choose to include your top two topic interests and up to four saved answers. Page history, reading measurements, contact information and scope briefs are never included. With remembering off or Global Privacy Control enabled, guides use only explicit choices. Optional questions also contribute to combined counts, as explained below. Review, remove or clear saved items before sharing a device.

Click the Piton Security logo in the header to return home and clear this tab’s learning queue. Your remembering preference stays the same.

Question counts

Optional questions report totals for displays, answers, dismissals, and scroll-pasts. Piton stores totals by question and answer option, without visitor IDs or individual event histories. These totals are not sent to an AI provider. “Turn this off” and Global Privacy Control stop reports. Clearing this browser cannot undo a contribution already combined into a total.

Show the stored data